影子 IT 建立云环境的速度引起了 IT 和安全团队的关注。寻找安全盲点有助于将一些问题置于焦点上。
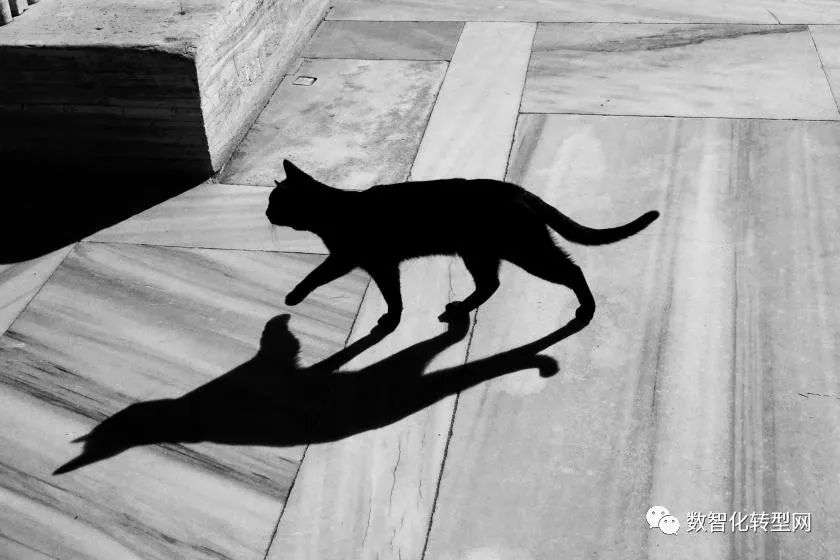
当攻击面不断扩大时,保护组织免受网络威胁和攻击变得越来越困难。除了这种扩展之外,影子 IT 的增长也是不可否认的——当组织及其部门(想想开发、财务、法律、营销等)在 IT 和安全团队的职权范围之外使用基础设施和服务时。这些不受监管的服务包括新的业务基础设施、托管合作伙伴、SaaS 服务、员工的连接应用程序、低代码/无代码软件平台等。
Gartner 发现,影子 IT 占企业组织 IT 支出的 30% 到 40%,这使其成为一个持续的挑战。
一、影子 IT 安全风险
在影子 IT 激增的公司中,有多种云服务正在使用中,并且这些服务经常相互关联。设置云环境很容易,再加上许多环境的构建和设置(有些环境是自动基于脚本的),IT 和安全团队必须急于跟上由此产生的不断增长的攻击面。
DevOps 经常在不知不觉中从影子 IT 中产生安全风险。让我们举个例子,一个开发人员通过启动云基础设施来建立自己的服务。这可以使用公司云提供商的主帐户或通过许多其他方法完成,这些方法使开发人员的工作变得轻松,但 IT 难以跟踪。
也许这些服务在一段时间后就闲置了,但它们仍保留在公司的云环境中。接下来,攻击者找到该服务,并查看基础资产是否受到保护。攻击者通常会寻找与公司资产相关的弱点,这些弱点本应退役,或者不属于 IT 部门已知和管理的人员的职权范围。将其乘以组织中的开发人员数量,然后乘以云应用程序的数量,问题就会增加。事实是,IT 部门可能根本不了解正在使用的云资产。
正如我们现在所知,通过采用公有云平台,组织比以往任何时候都更容易扩展和加速 IT 运营。但是,随着组织的云攻击面变得越来越复杂且更难监管,攻击者可以更容易地利用云错误配置或暴露的漏洞。
二、攻击者的观点
在服务器和服务流动的多云环境中,安全监督通常无法完成工作。这会导致盲点、未识别和未检查的设备和数据。
根据 ESG Research 对网络安全专业人士的调查,76% 的人表示,他们因未知、未管理或管理不善的面向互联网的资产而遭受过网络攻击。近四分之三的企业(73%)认为他们对不到80%的资产有强烈的意识。这意味着五分之一的面向互联网的资产是可能容易受到攻击的盲点。
在当今的安全环境中,所有组织都需要积极主动,并拥有 365 度视图,以便从攻击者的角度查看云。外部攻击面管理是实现该视图的强大工具。这使组织能够暴露威胁,而不仅仅是资产,从而主动保护整个数字供应链。
当今的组织需要奠定基础,将影子 IT 识别为这种不断扩大的攻击面的一部分。基金会包括:
- 持续准确的资产发现。 如果资产在不断变化,持续监控和发现是降低风险的第一步。一个组织需要知道它拥有哪些资产来保护它们。
- 围绕业务关键型资产的上下文。一旦您了解了完整的互联资产清单并持续监控变化,那么决策时间就到了。这些资产中哪些是关键任务?包含敏感的公司、客户、合作伙伴或个人信息。为了应用适当的保护措施,需要将对 IT 资产的理解映射到它们对业务的重要性。
- 第三方资产。 这不仅仅是关于你拥有的资产。在当今互联互通的数字世界中,贵组织的第三方软件以及供应商管理和维护的资产的扩展网络。攻击者经常利用这些资产和连接来访问组织中的最终目标。因此,从数字供应链中绘制攻击路径是获取攻击者视图的关键部分。
有了这些部分,就可以减少或消除盲点,影子 IT 可以变得不那么可怕,并且可以采取主动行动来减少攻击面和组织面临的安全风险。
英文原文:
How a Focus on Security Blind Spots Can Force Shadow IT out of the Darkness
The speed at which shadow IT can set up cloud environments is cause for concern for IT and security teams. Looking for security blind spots can help put some of the issues into focus.
It’s getting harder to secure your organization from cyber threats and attacks when the attack surface is continuously expanding. Adding to this expansion is the undeniable growth of Shadow IT – when infrastructure and services are used by an organization and its departments (think dev, finance, legal, marketing, and more) outside the purview of the IT and security teams. These ungoverned services include new business infrastructure, hosting partners, SaaS services, employees’ connected apps, low-code/no-code software platforms, and more.
Gartner found that shadow IT is between 30% and 40% of IT spending in enterprise organizations, making it a constant challenge.
1. Shadow IT Security Risks
In a company where shadow IT proliferates, often several cloud services are in use, and these are frequently linked. There is an ease to setting up cloud environments, and coupled with the building and setting up of many environments – some automatically based on scripts – IT and security teams must rush to keep up with the growing attack surface this creates.
DevOps is often unwittingly creating security risks from shadow IT. Let’s take, for example, a developer who sets up their own service by spinning up cloud infrastructure. This can be done using a master account of the company’s cloud provider or via many other methods that make life easy for developers but difficult for IT to track.
Perhaps these services are unused after some time, but they remain in the company’s cloud environment. Next, an attacker finds that service and looks to see if the underlying asset is protected. Attackers often seek out weaknesses related to the company’s assets that should have been decommissioned or that fall outside the purview of those known and managed by IT. Multiply this by the number of developers in an organization and then by the number of cloud applications, and the problem increases. The fact is that an IT department may simply not be aware of the cloud assets in use.
As we now know, it’s easier than it has ever been for organizations to scale and accelerate IT operations by adopting public cloud platforms. But, as an organization’s cloud attack surface becomes more complex and more difficult to oversee, attackers can exploit cloud misconfigurations or exposed vulnerabilities more easily.
2. An Attacker’s Point of View
In a multi-cloud environment, where servers and services are fluid, security oversight often can’t get the job done. This leads to blind spots, unidentified and unchecked devices, and data.
According to an ESG Research survey of cybersecurity professionals, 76% say they’ve experienced a cyberattack because of an unknown, unmanaged, or mismanaged internet-facing asset. Nearly three-quarters of enterprises (73%) believe they have a strong awareness of less than 80% of their assets. This means that 1 in 5 internet-facing assets are blind spots that could be vulnerable to attack.
In today’s security environment, all organizations need to be proactive and have a 365-degree view to see the cloud from an attacker’s point of view. External Attack Surface Management is a powerful tool to achieve that view. This enables an organization to expose threats and not just assets to proactively defend the full digital supply chain.
Organizations today need to lay a foundation to identify Shadow IT as a part of this ever-expanding attack surface. The foundation includes:
- Continuous and accurate asset discovery. If the assets are constantly changing, continuous monitoring and discovery is step one to reducing risk. An organization needs to know what assets it has in order to protect them.
- Context around business-critical assets. Once you have gained visibility into your complete inventory of connected assets and are monitoring continuously for changes, then comes decision time. Which of these assets are mission critical? Which contain sensitive corporate, customer, partner, or personal information. In order to apply the proper protections, an understanding of IT assets needs to be mapped to their importance to the business.
- Third-party Assets. It’s not just about the assets you own. In today’s interconnected digital world – your organization’s extended network of third-party software and vendor-managed and maintained assets. Attackers often exploit these assets and connections to gain access to their ultimate target in your organization. Therefore, mapping attack paths from the digital supply chain is a crucial part of gaining the attacker’s view.
With these pieces in place, blind spots can be reduced or eliminated, Shadow IT can become a little less scary, and proactive actions can take place to reduce the attack surface and the security risks facing an organization.